The use case: how Auth0 deploys Snyk
Auth0's product security team uses Snyk Open Source and Snyk Container to find and prioritize vulnerabilities in open source dependencies. They packaged Snyk in a security container within the Docker development environment so engineers can run scans themselves.
In the customer’s words
The Auth0 team uses Snyk to make sure we are running on a secure foundation, no matter what.Other AI tools used by Auth0
Other public relationships recorded on usedby.
Explore Auth0’s AI stack
Snyk users in Cybersecurity
Companies in the same sector, with public evidence.
See all Snyk customers
Go straight to the source
Based on Snyk’s published case study. We check the public evidence; the results are reported by the vendor.
snyk.io- Last checked
- Nov 10, 2026
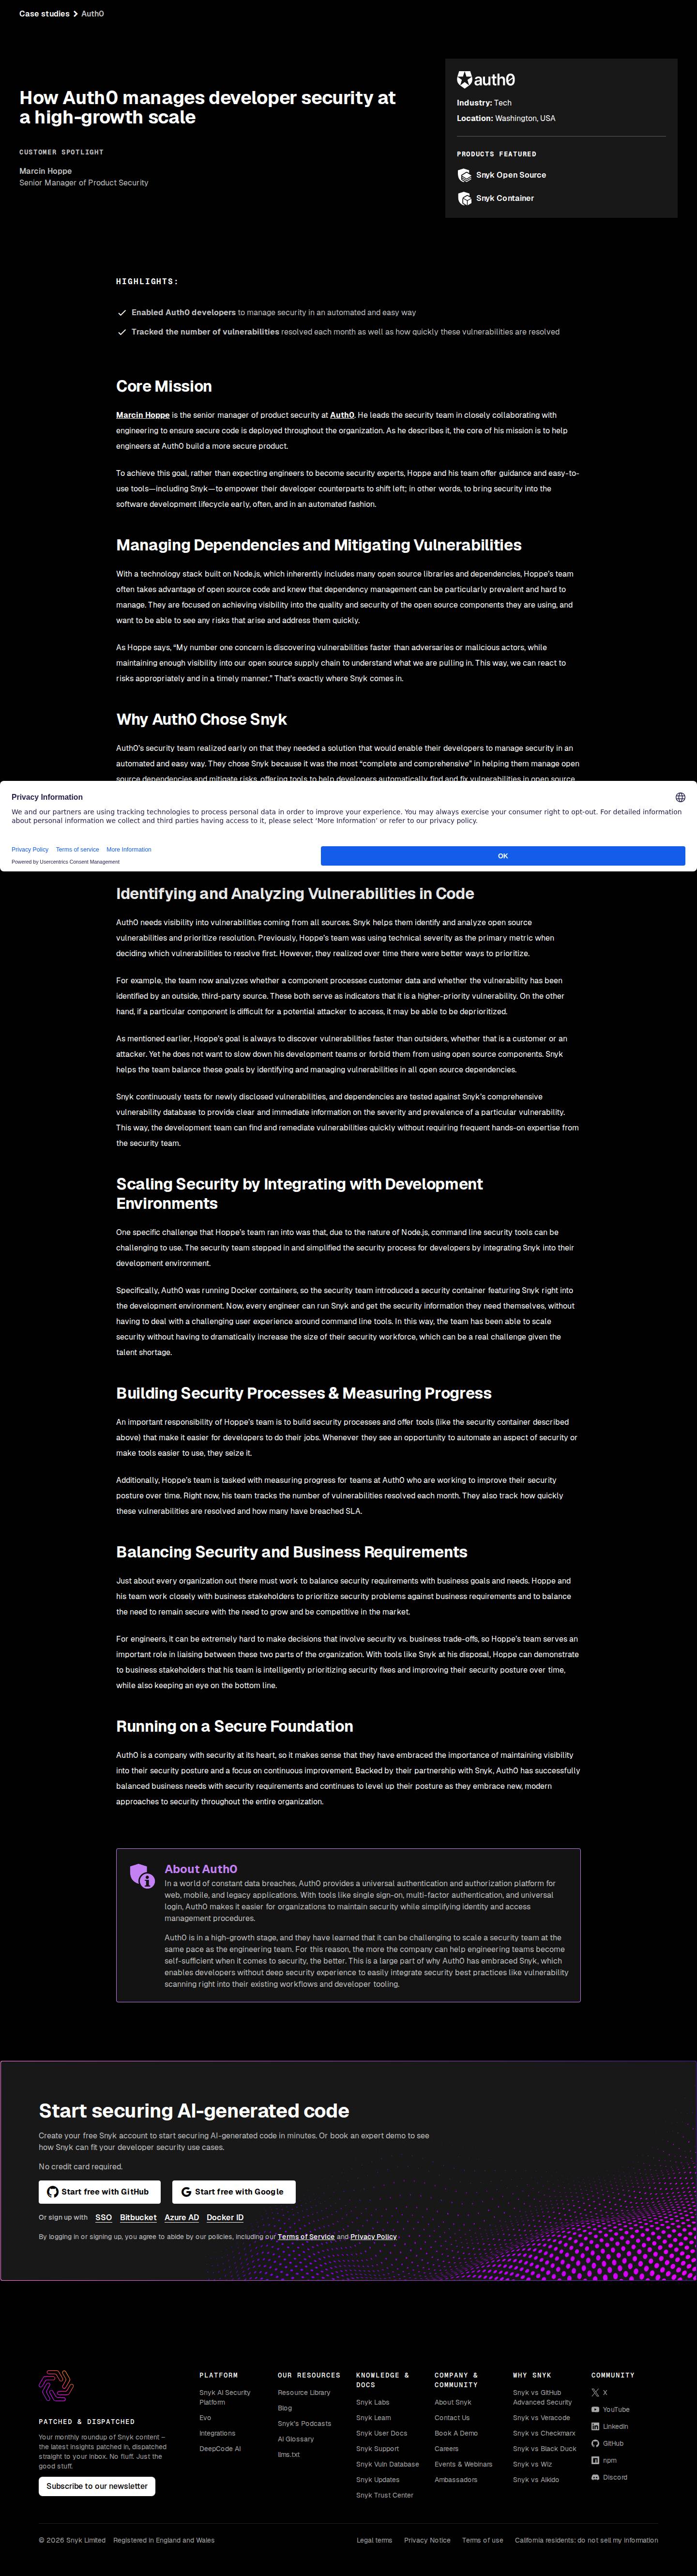 Open source capture
What the story claims, and what we checked
What we compared with the page.
- The passage quoted aboveChecked
Copied word for word from the page, near the name of Auth0.
- Auth0 uses SnykChecked
Confirmed line.
- The result itselfNot checked
We quote it; we did not measure it.
Now, every engineer can run Snyk and get the security information they need themselves, without having to deal with a challenging user experience around command line tools. In this way, the team has been able to scale security without having to dramatically increase the size of their security workforce