The use case: how Reach deploys Omnea
Reach uses Omnea as a single platform for procurement intake, supplier management and third-party risk management. Risk assessments are embedded in procurement workflows, with suppliers submitting questionnaires through a portal and AI capturing supplier risks.
More reported results
Figures published in Omnea’s case study. They are not independently measured by usedby.
Reach has moved from reactive to proactive TPRM — with Omnea AI automatically capturing 70% of supplier risks, improving data accuracy, consistency, and audit readiness.
Maverick spend reduced from 30% to 5%
£100K+ annual savings from consolidating 4 tools into 1
~15% reduction in long-tail supplier base
In the customer’s words
Before Omnea, risk lived in its own silo — detached from procurement and difficult to contextualise. Now, everything is in one place. We can see the cyber, legal, and financial risk associated with a supplier in a single view, giving the business real clarity. It's helped us move from fragmented approvals and spreadsheet assessments to a joined-up process with a clean audit trail. That integration isn't just efficient — it's essential for understanding and actively managing risk.We’ve reduced manual effort by over 70%, consolidated four systems into one. What used to take days now takes minutes.Other AI tools used by Reach
Other public relationships recorded on usedby.
Explore Reach’s AI stack
Other companies using Omnea
Customers across industries, with public evidence.
 AdyenConfirmed
 EntrustConfirmed
 FactorialConfirmed
 Hargreaves LansdownConfirmed
 Just Eat Takeaway.comConfirmed
 McAfeeConfirmed
Go straight to the source
Based on Omnea’s published case study. We check the public evidence; the results are reported by the vendor.
omnea.co- Source published
- Aug 16, 2026
- Last checked
- Nov 12, 2026
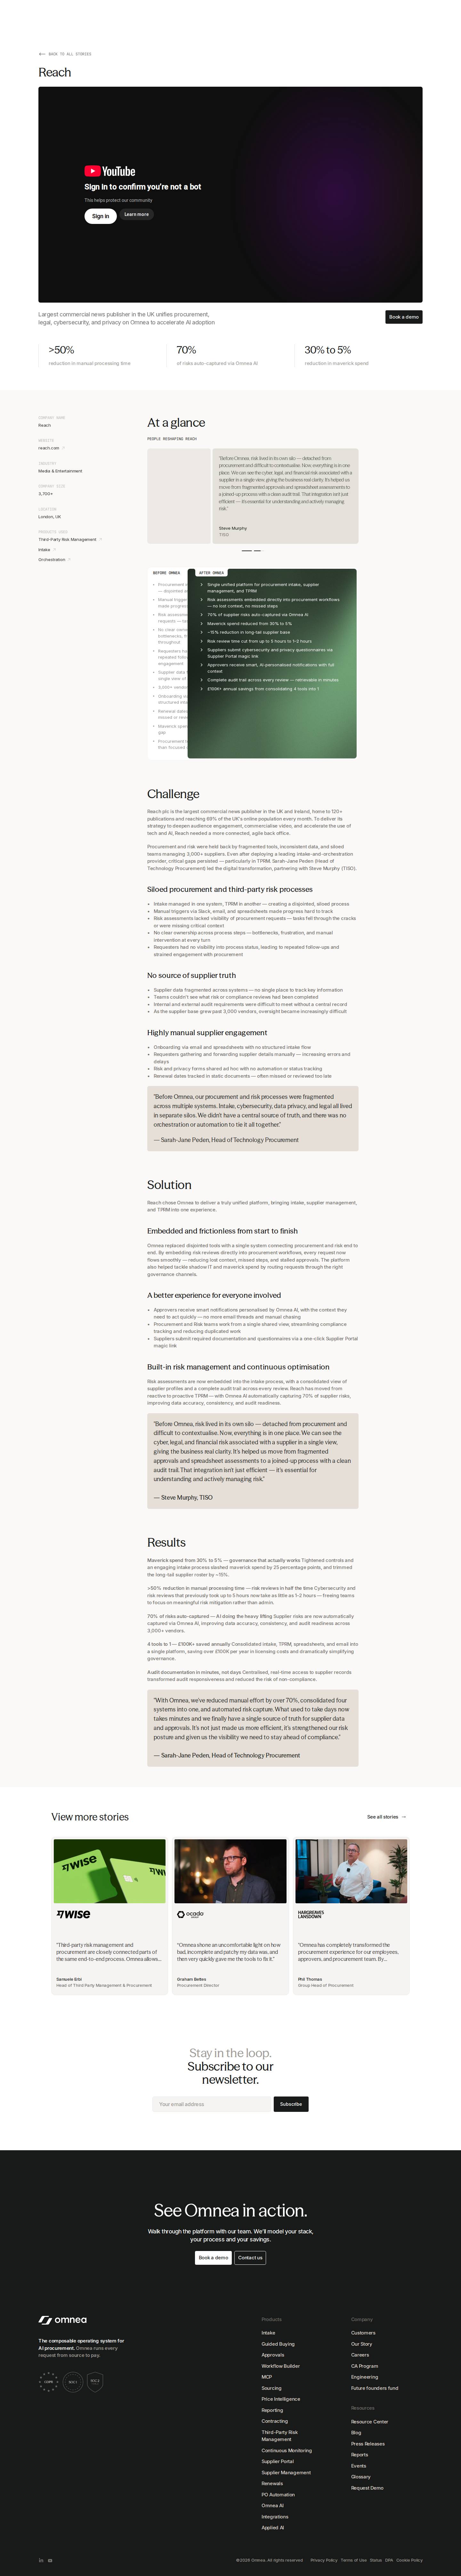 Open source capture
What the story claims, and what we checked
What we compared with the page.
- The publication dateChecked
Read from the page’s own metadata, never guessed.
- Reach uses OmneaChecked
Confirmed line.
- The result itselfNot checked
We quote it; we did not measure it.
Cybersecurity and risk reviews that previously took up to 5 hours now take as little as 1–2 hours — freeing teams to focus on meaningful risk mitigation rather than admin.