The use case: how MongoDB deploys Snyk
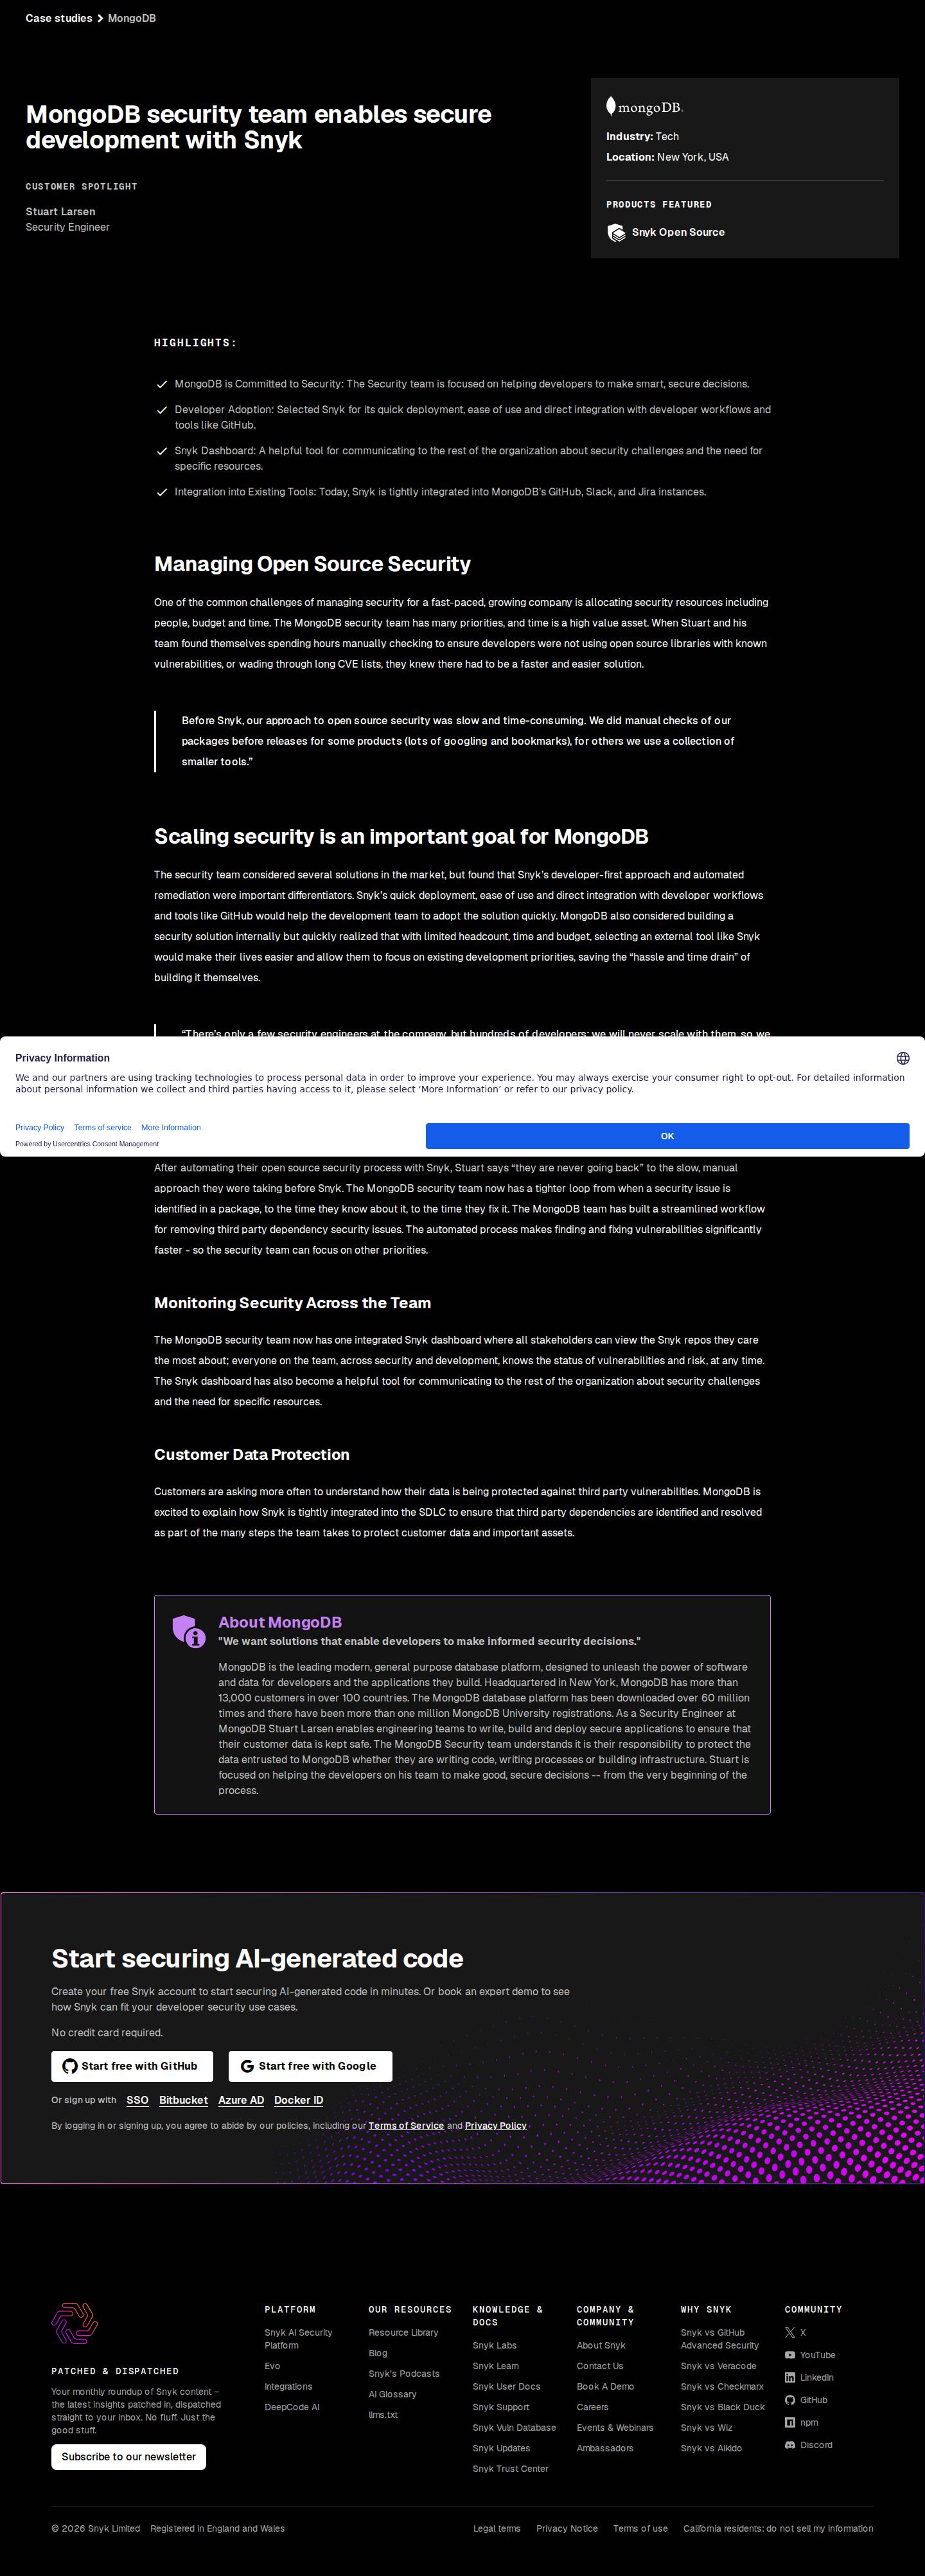
MongoDB's security team uses Snyk Open Source to automatically find and fix known vulnerabilities in third-party open source dependencies, replacing manual package checks before releases. Snyk is integrated with GitHub, Slack and Jira, and its dashboard gives security and development staff shared visibility into vulnerability status.
In the customer’s words
There’s only a few security engineers at the company, but hundreds of developers; we will never scale with them, so we must proactively enable them.Other AI tools used by MongoDB
Other public relationships recorded on usedby.
Explore MongoDB’s AI stack
Snyk users in Data & Analytics
Companies in the same sector, with public evidence.
See all Snyk customers
Go straight to the source
Based on Snyk’s published case study. We check the public evidence; the results are reported by the vendor.
snyk.io- Last checked
- Nov 10, 2026
 Open source capture
What the story claims, and what we checked
What we compared with the page.
- The passage quoted aboveChecked
Copied word for word from the page, near the name of MongoDB.
- MongoDB uses SnykChecked
Confirmed line.
- The result itselfNot checked
We quote it; we did not measure it.
After automating their open source security process with Snyk, Stuart says “they are never going back” to the slow, manual approach they were taking before Snyk. The MongoDB security team now has a tighter loop from when a security issue is identified in a package, to the time they know about it, to the time they fix it.