The use case: how Thoughtworks deploys SentinelOne
Thoughtworks deployed SentinelOne's Singularity Endpoint on all of its endpoints to replace legacy endpoint protection. It uses the platform for autonomous threat detection, behavioral monitoring, and automated containment and remediation, with analysts investigating and threat hunting from a single view when human review is needed.
In the customer’s words
The same analysts who were triaging alerts are now able to threat hunt and deliver more value.Other AI tools used by Thoughtworks
Other public relationships recorded on usedby.
Explore Thoughtworks’s AI stack
Other companies using SentinelOne
Customers across industries, with public evidence.
 10x BankingConfirmed
 Aston MartinConfirmed
 Barry-WehmillerConfirmed
 Capital Area Intermediate Unit (CAIU)Confirmed
 Carnival CorporationConfirmed
 City of Los AngelesConfirmed
Go straight to the source
Based on SentinelOne’s published case study. We check the public evidence; the results are reported by the vendor.
sentinelone.com- Source published
- Mar 5, 2026
- Last checked
- Oct 5, 2026
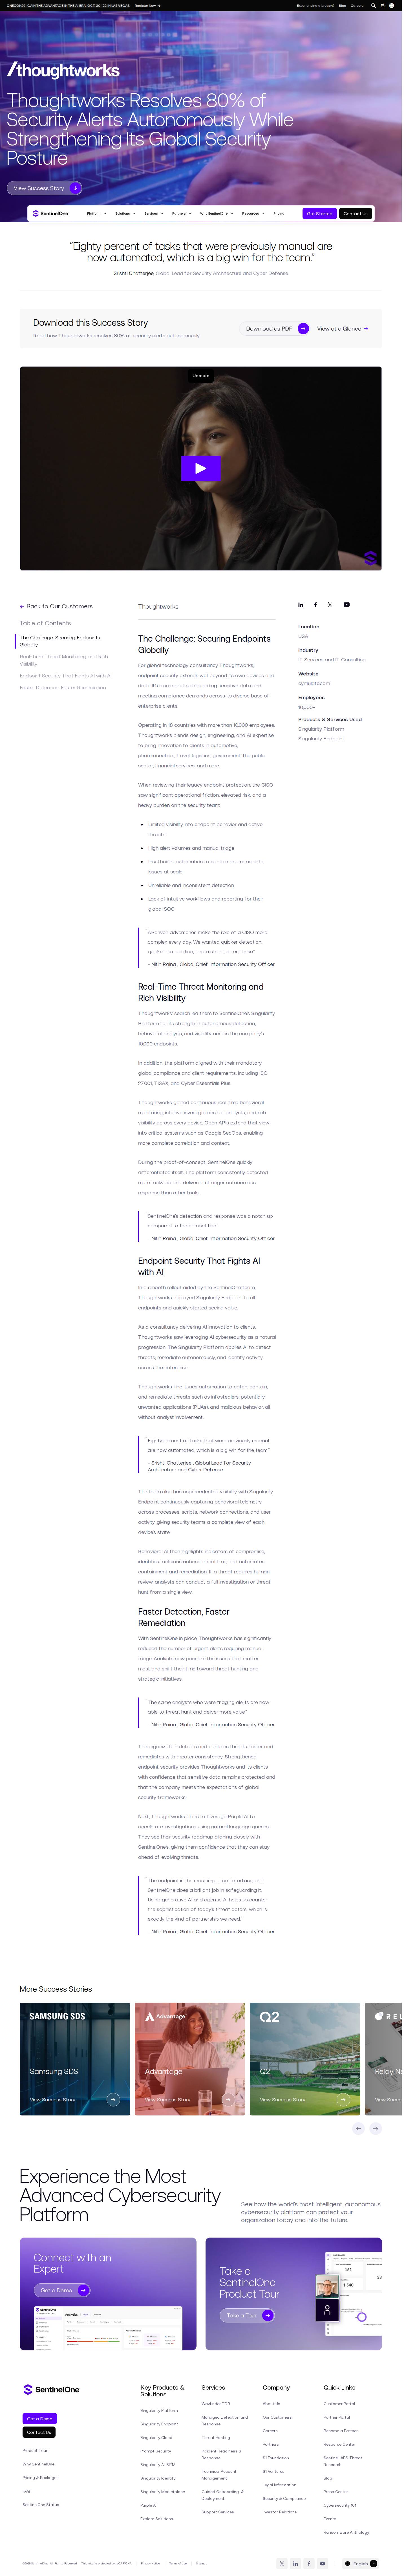 Open source capture
What the story claims, and what we checked
What we compared with the page.
- The figure: 80%Checked
The figure is on the page; its label is our wording.
- The passage quoted aboveChecked
Copied word for word from the page, near the name of Thoughtworks.
- The publication dateChecked
Read from the page’s own metadata, never guessed.
- Thoughtworks uses SentinelOneChecked
Confirmed line.
- The result itselfNot checked
We quote it; we did not measure it.
Thoughtworks fine-tunes automation to catch, contain, and remediate threats such as infostealers, potentially unwanted applications (PUAs), and malicious behavior, all without analyst involvement.